Governance & Risk
Review boards, attestations, data quality, controls, and change control.
Architecture governance in Arvane is designed to gate go-live decisions without turning the tool into an ITSM system or a cloud provisioner.
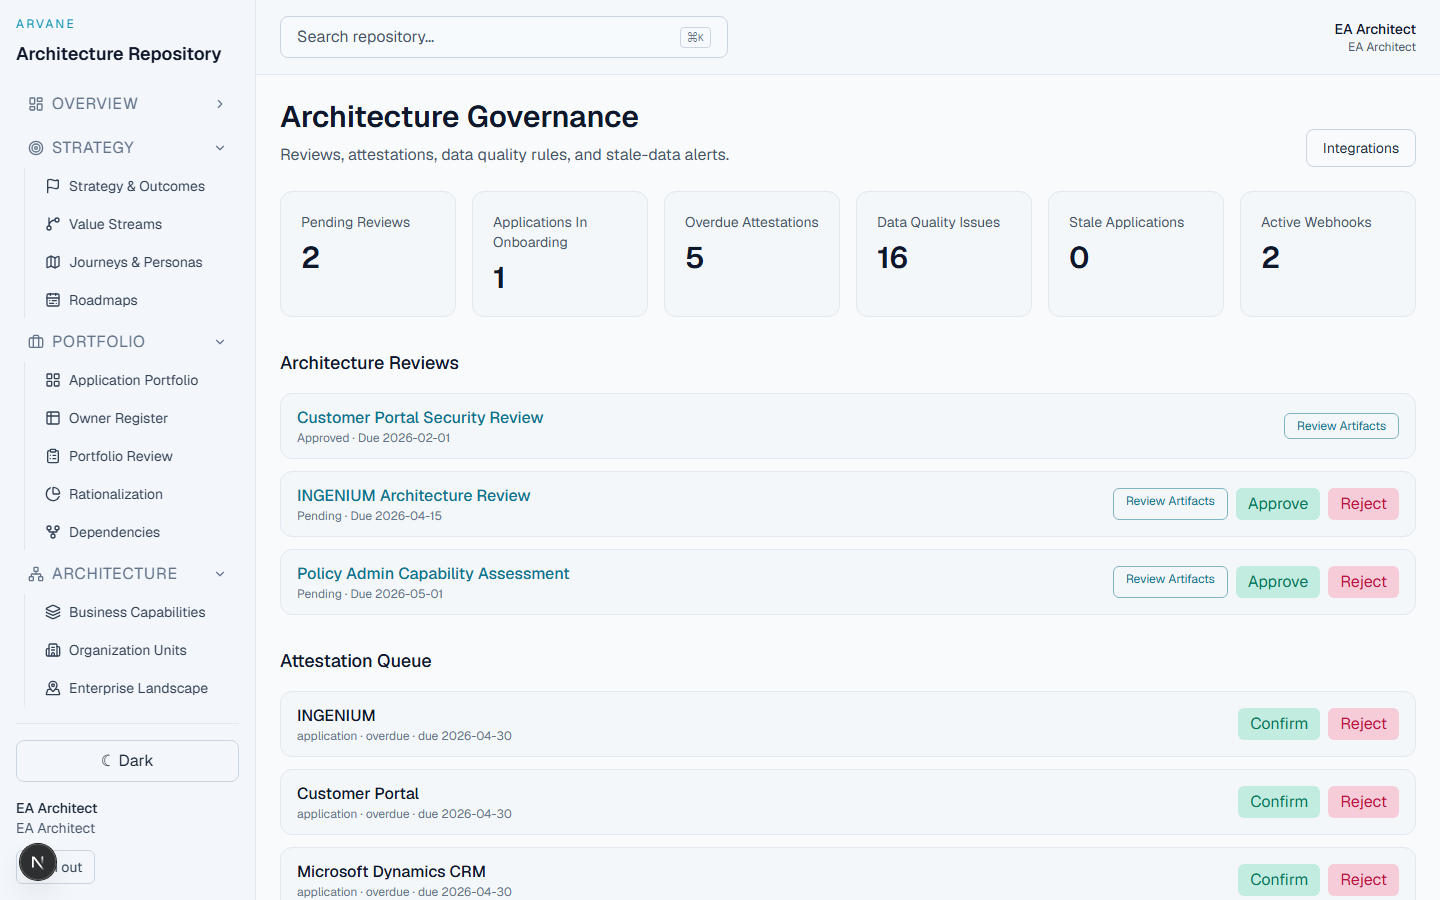
Governance
/governance covers ARB reviews, an attestation queue, and data quality
violation tracking.
Application Onboarding
Dual-track architecture and application checklists with automatic ARB creation, an AI usage declaration step, evidence document attachments per checklist item, and a centralized Documents tab with tag filtering. Checklist steps and mandatory document rules are configurable at Configuration.
Security Assessment
/governance/security-assessment is a filterable inventory of every
application's security assessment — due dates, outcomes, and evidence
artifacts. The same assessment appears as its own tab on the application
detail page, ahead of Onboarding and Recertification.
Recertification
/governance/recertification is a filterable portfolio table with
readiness bars, workflow-stage pills, and next-review dates.
Recertification moves through draft → owner update → ARB review → certified on a 365-day cadence, and feeds directly into each application's
ARB completeness score.
A npm run seed:compliant-sample script (optional — not part of the default
seed:all) seeds a fully compliant reference record — 100% ARB
completeness, completed onboarding, a compliant security assessment with
evidence, and a certified recertification — useful as a "what good looks
like" example.
Surveys
/governance/surveys runs fitness and usage campaigns; overdue campaigns can
automatically create attestations.
Change & Release
/governance/change tracks infrastructure provisioning requests and
production promotions through a draft → submitted → approved | rejected
flow, plus go-live checklist execution.
- Approving a promotion sets the application's status to Production and its
productionDateif empty; completing the checklist marks the request completed - Approving an infra request records the decision only — Arvane does not call
Terraform or any cloud API — and emits a
change.infra.approvedwebhook - Webhooks fire on
change.request.created,change.infra.approved, andchange.promotion.approved, with Jira/CMDB/generic connector templates
AI Governance
/ai-governance maintains an AI system inventory with EU AI Act-style risk
tiers, NIST AI RMF and DORA compliance scoring, shadow AI detection, policies,
and human-oversight flags.
GRC Controls
/grc is a control catalog with test evidence, for teams that need formal GRC
tracking alongside architecture governance.
Related
- Onboarding & Application Assurance — the readiness check and evidence templates that feed into onboarding and ARB review
- Strategy & Roadmaps — governance reviews triggered by roadmap-driven change